Beyond Purdue / Resilience, Cybersecurity
A $5 Cable. 12,000 Controllers. One Black Swan.
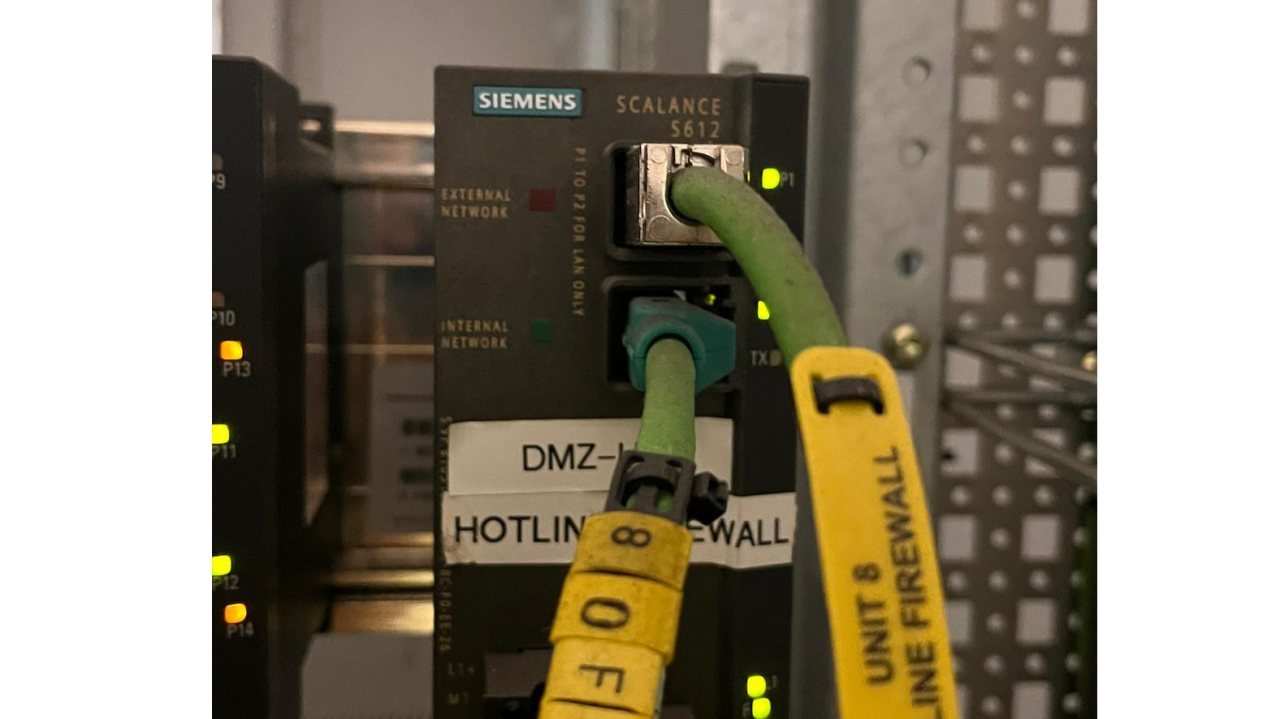
Just imagine: At one of the largest solar power plants in the Gulf, over 12,000 Siemens S7-1200 controllers — popular, cheap, and critically vulnerable — were deployed across dozens of systems.
- It didn’t come from the Internet.
- It didn’t come from China. It didn’t come from AI.
It came from a technician with a toolbag, a tired shift handover, and a USB cable that never should’ve been there.
That’s all it took.
Just imagine: At one of the largest solar power plants in the Gulf, over 12,000 Siemens S7-1200 controllers — popular, cheap, and critically vulnerable — were deployed across dozens of systems.
What happened wasn’t theoretical. It was operational.
- A malformed broadcast packet — even accidental — locked every controller in seconds.
- Control logic halted.
- Loops tripped.
- HMI screens froze.
- OPC servers went silent.
- And a few engineers, at the end of a long shift, were suddenly the only hope.
There was no documentation. No map. No backup of logic files.
Just sweat, sun, and 12,000 cabinets waiting for a hard reset.
The Real Problem Isn’t the Vulnerability — It’s the Inaction
This wasn’t a zero-day. This wasn’t an attacker. This was a known flaw — and a complete lack of preparation.
And that’s the real risk.
Plants spend months waiting for vendors, proposals, and compliance mappings — while logic goes unbacked, passwords stay default, diagrams disappear, and undocumented controllers run critical processes.
A single misstep — and you're blind.
That’s not cybersecurity. That’s delay disguised as planning.
And by the time the paperwork is done, the plant may already be offline — with engineers holding a flashlight and a laptop full of outdated firmware.
What Should Have Been Done?
Cybersecurity isn’t about firewalls and buzzwords
Cybersecurity isn’t about ROI (Return On Investment)
It’s about:
- Documenting the assets
- Backing up the logic
- Knowing which controller runs what
- And preparing for that moment when the unexpected becomes reality
- Its about Business Continuity
At Bohemia Market, we start with the basics:
Maintenance & Cybersecurity Datasheets Physical risk assessments — even if the EPC didn’t finish theirs 20+ chapter Cybersecurity Handbook (NESA, ISO 27001, DEWA-aligned) And above all — Business Continuity as the goal
Because when it all locks up… no one asks for a certificate. They ask: “Where’s the backup?” And: “Who can get this online again?”
Your Next USB Moment
We’ve built the ICS Secure Data Transfer platform not just to defend from attacks, but to survive random failures — those quiet black swans that don’t look like cyber at all.
So ask yourself: What’s your next USB moment?
And when it happens, will you be chasing OEMs for documents — or walking straight to the right cabinet?
📖 More on this in our Beyond Purdue series: https://www.linkedin.com/newsletters/beyond-purdue-7315971708727808000
🎯 Want to test your plant’s readiness? Try our online quiz: https://quizzes.bohemiamarket.com/securedatatransfer
🔗 Watch what failure really looks like: https://www.linkedin.com/posts/petrroupec_back-to-90s-security-through-obscurity-activity-7189849509680627712-xAvB