Beyond Purdue No. 023 / Supply chain, Cybersecurity
Supply chain attack
A supply chain attack is an attack that targets an organization by compromising a trusted third-party vendor, partner, or supplier in the supply chain. Rather than attacking an organization...
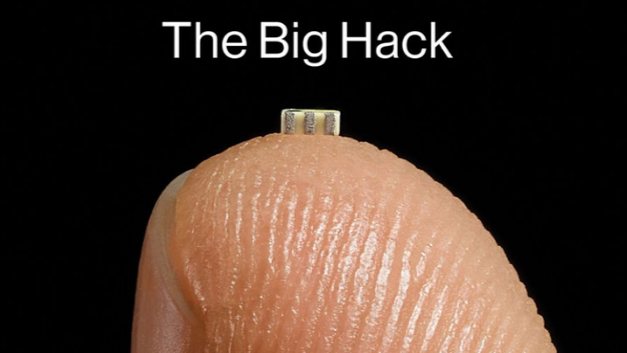
A supply chain attack is an attack that targets an organization by compromising a trusted third-party vendor, partner, or supplier in the supply chain. Rather than attacking an organization directly, attackers exploit these trusted third-party relationships to infiltrate the target’s systems or data, often without immediate detection.
How Supply Chain Attacks Work
Attackers look for weaknesses in any connected third-party—such as software providers, managed service providers, or other business partners—and use them as entry points to distribute malware or steal data. Common attack vectors include:
- Malicious code in software updates: Attackers insert malware into legitimate software or updates distributed by the vendor—when customers install these updates, their systems get compromised.
- Compromised cloud or IT service providers: Gaining access to shared platforms can expose multiple customers connected through the same provider.
- Hardware or firmware backdoors: Tampering with hardware during manufacturing or shipping to introduce vulnerabilities at the hardware level.
Examples
- SolarWinds (2020): Attackers implanted a backdoor in a software update for SolarWinds' Orion platform, affecting 18,000 customers, including major US government agencies
- Modified communication devices (2024): Mossad managed to insert explosives into pagers by creating a fake company that partnered with legitimate manufacturers. These tampered pagers were then sold through regular suppliers to Hezbollah, who unknowingly distributed weaponized devices to their members.
- Stuxnet: Stuxnet is a famous example of a cyber attack that targeted industrial control systems by exploiting the software supply chain. In this case, attackers developed a sophisticated worm that specifically searched for Siemens PLC controllers running in Iran’s Natanz nuclear facility. The malware was delivered—most likely via infected USB drives—bypassing air-gapped security by leveraging trusted connections and stolen digital certificates from legitimate vendors, which made detection extremely difficult
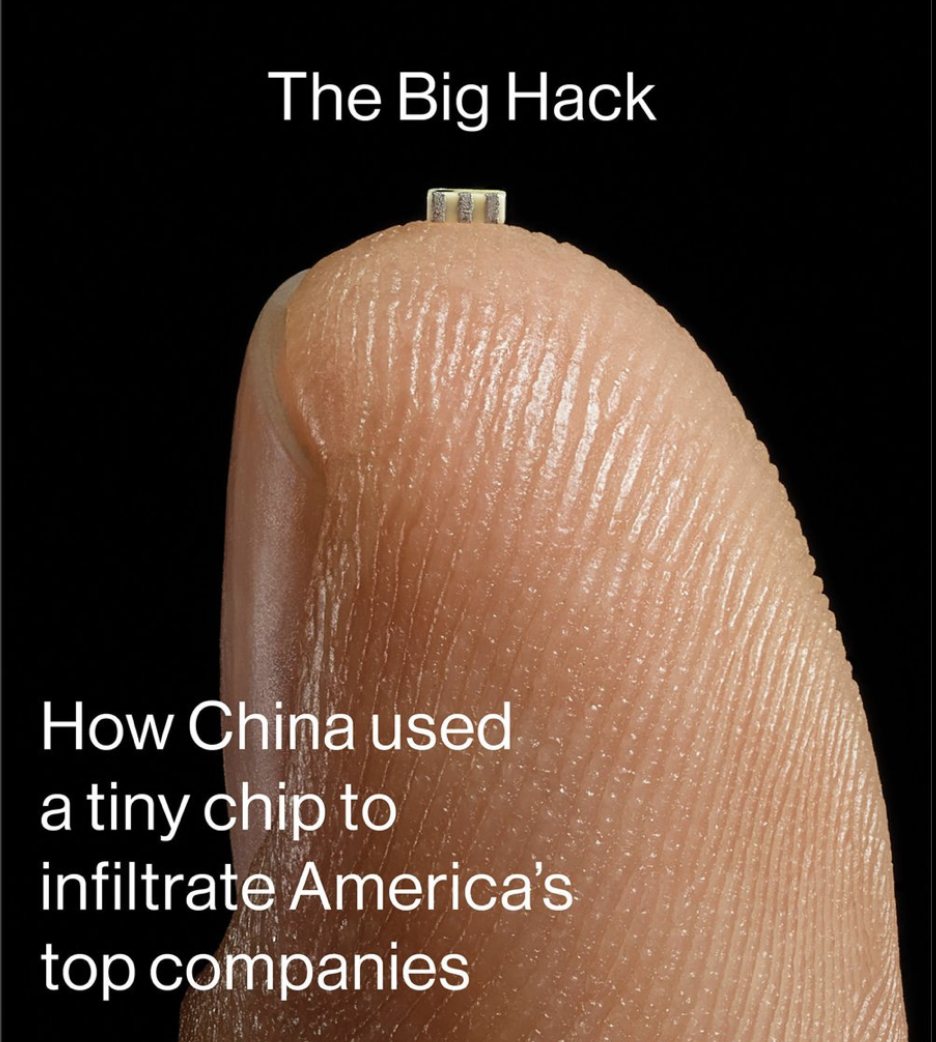
- China Used a Tiny Chip to Infiltrate U.S. Companies The attack by Chinese spies reached almost 30 U.S. companies, including Amazon and Apple, by compromising America’s technology supply chain, according to extensive interviews with government and corporate sources
Impact of Supply Chain Attacks
- Operational Disruption: Critical operations may be halted, leading to disruptions and significant financial losses
- Widespread Damage: Because one compromised vendor can impact all of its customers, these attacks have a large “blast radius” and can trigger global incidents
- Reputational and Legal Impact: Breaches often result in loss of customer trust, legal actions, and regulatory fines for affected organizations
Why They’re Hard to Prevent? They are Black Swans
Supply chain attacks exploit deep trust relationships and the complexity of software ecosystems. They can remain undetected for long periods because updates or connections come from known, legitimate sources—making traditional cybersecurity tools less effective.
Recommended by LinkedIn
Official Prevention Strategies - what they they say
Vendors, government, laws, standards say – fix, fix, update, upgrade
- Vet and monitor third-party vendors for robust security practices
- Limit third-party access to only what's necessary.
- Continuously monitor for anomalies or unusual activity in the supply chain.
- Rapidly install critical security patches and updates, especially when supply chain compromises are disclosed
Supply chain attacks demonstrate that security is only as strong as the weakest link, making vendor management and oversight crucial for all organizations. Any modification is new black swans entering thought front door.
The only problem? It does not work !
New system, new vulnerabilities, new black swans entering thought front door
New hardware, new vulnerabilities, new errors, new black swans entering thought front door
New update, new errors, incompatibilities, new black swans entering thought front door
And each and every patch, upgrade is, new black swans entering thought front door.